

ACERCA DE ESTE EPISODIO
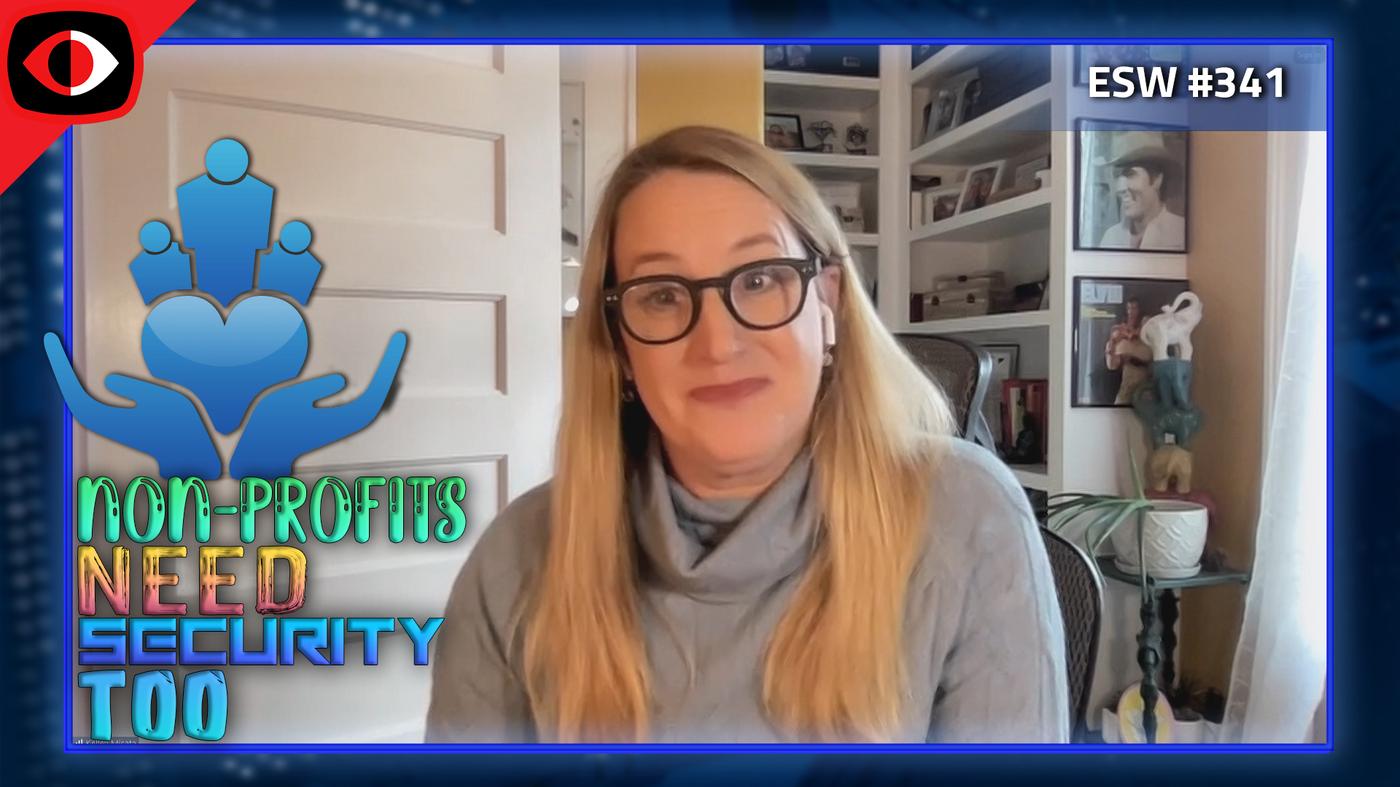
While non-profit doesn't mean "no budget" when it comes to cybersecurity, a lot of smaller to mid-sized non-profits operate on a shoestring, with little to no money for cybersecurity talent or spending. This is where Sightline Security steps in. Sightline's founder and CEO, Kelley Misata joins us today to explain how her own non-profit helps other non-profits improve their cybersecurity posture.
As with any category of trends, the success rate of cybercrime ebbs and flows. As Russia seems be a safe haven for cybercriminals, it seemed for a while that the war in Ukraine might disrupt this activity. It did, but only for a short while.
Keith Jarvis walks us through the latest types, tactics, and trends in cybercrime. Secureworks' latest State of the Threat report reveals a disturbing dichotomy: how is it we understand our adversaries' so well, but continue to fail to stop them? In this interview, we aim to understand what needs to happen to tilt the odds a bit back in our favor.
Segment Resources:
Segment description coming soon!
Visit https://www.securityweekly.com/esw for all the latest episodes!
Follow us on Twitter: https://www.twitter.com/securityweekly Like us on Facebook: https://www.facebook.com/secweekly
Visit https://www.securityweekly.com/esw for all the latest episodes!
Follow us on Twitter: https://www.twitter.com/securityweekly Like us on Facebook: https://www.facebook.com/secweekly
Show Notes: https://securityweekly.com/esw-341


