
ACERCA DE ESTE EPISODIO
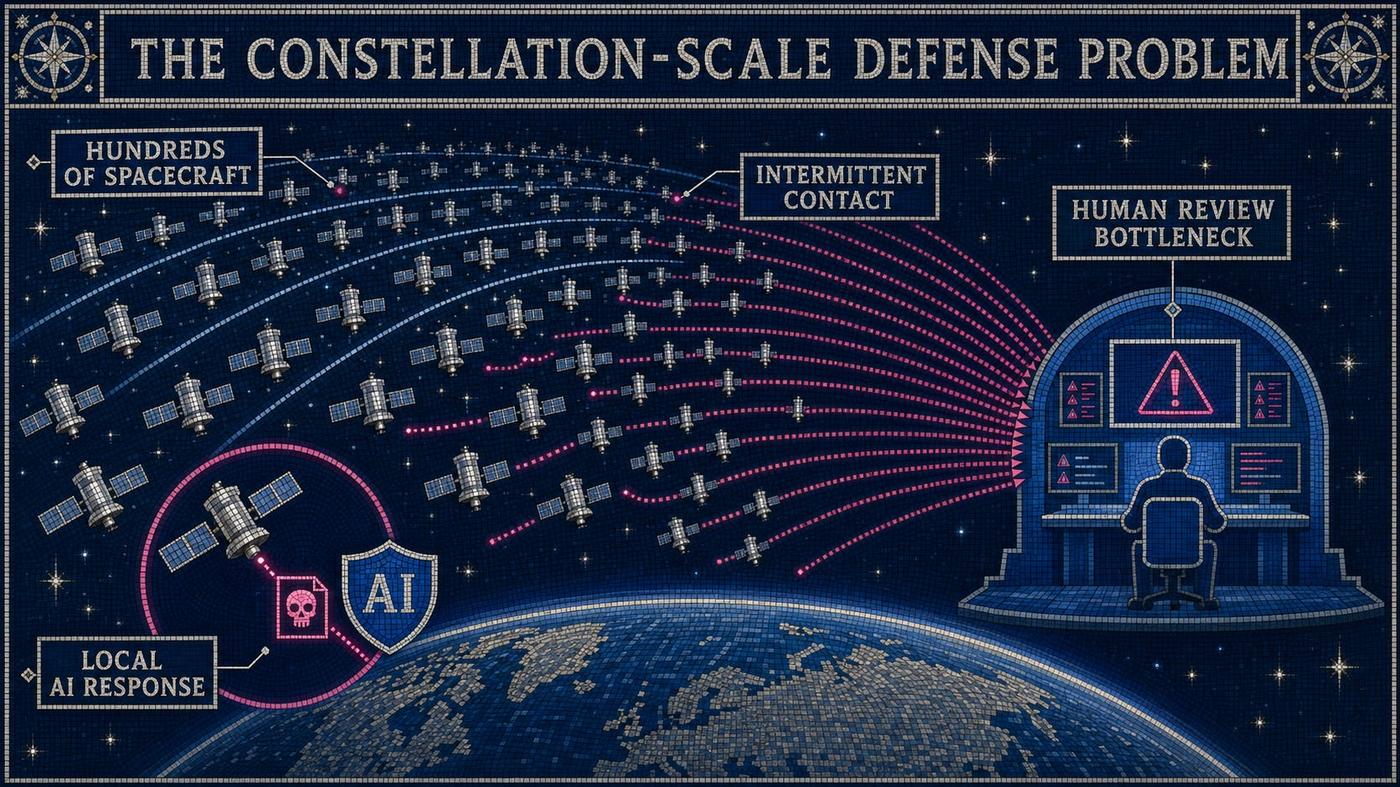
Large satellite constellations are approaching a scale at which human operators cannot investigate every suspicious event within an operationally useful period. A proliferated fleet may produce an immense stream of authentication records, command histories and software alerts. Its spacecraft will also pass through intermittent contact windows. By the time a ground team understands an anomaly, malicious activity may have crossed a satellite link or reached another part of the mission system.
Artificial intelligence offers a plausible response to this timing problem. An onboard or ground-based defensive agent could establish a picture of normal behavior, identify an anomalous command sequence and restrict a suspect credential before the threat spreads. NASA already requires certain missions to consider autonomous telemetry monitoring for unexplained interference under its Space System Protection Standard. The technical step from monitoring to automated containment is substantial, but the operational pressure behind it is clear.
The central difficulty concerns authority rather than detection accuracy alone. Finding a cyber anomaly is an analytic act. Isolating a spacecraft changes the mission architecture. A quarantine might preserve the constellation by containing a genuine compromise. A false alarm could remove a healthy satellite during combat. An adversary could also manufacture suspicious behavior in order to provoke the defender’s own system into denying service.
Autonomous cyber defense should therefore be treated as delegated command. Its permissions must be bounded by mission purpose. Its consequential actions should be reversible. Every automated intervention should create an intelligible record for human review. A separate rule-based safeguard should prevent the defensive model from exceeding a defined operational envelope. These controls impose friction, but friction is often wise when software is permitted to alter military capability.
The near-term path will favor narrow authority. Defensive agents will gain permission to revoke a credential, reject a malformed command or place a short hold on a crosslink. Broader powers will follow only after exercises show that these systems can contain actual threats without becoming an attacker’s remote control for self-inflicted mission loss.
The Operational Requirement for Machine-Speed Defense
The case for autonomy begins with constellation arithmetic. A fleet of several hundred spacecraft contains many endpoints whose software states change over time. Each vehicle participates in a larger mission system that includes a ground segment and external service providers. CISA’s Recommendations to Space System Operators for Improving Cybersecurity treats cyber risk across this full system because an attack does not need to begin in orbit. A compromised administrator account on Earth may become the path to a spacecraft command interface.
Traditional security operations assume that analysts can inspect an endpoint through a stable network connection. Orbital systems violate that assumption. A spacecraft may communicate with a particular ground station for only a short interval. The operator can receive an alert after the relevant event has already ended. This delay changes the value of speed. A brilliant diagnosis delivered after a malicious command has propagated is an autopsy with nicer stationery.
Autonomous defense can place judgment closer to the event. A local agent could compare a command against the spacecraft’s current state. It could determine whether the requesting identity normally issues that kind of command. If the sequence falls outside a permitted pattern, the agent could impose a temporary restriction. The response would occur while the anomaly remains containable.
NASA’s 2026 survey of Ground Data Systems and Mission Operations advises projects to incorporate security early in mission planning and points toward established NIST and CCSDS guidance. That engineering sequence matters. A mission cannot bolt autonomous defense onto the flight computer during its final security review. The vehicle needs trustworthy telemetry. The system needs a defined source of time. Command paths must expose enough context for the defensive agent to distinguish an unusual action from an impossible one.
Constellation scale also changes the purpose of automation. The aim is not to replace every analyst. It is to reserve human attention for decisions that warrant it. Software can process the first wave of routine anomalies. Human operators can examine the smaller set that carries serious mission consequences. This division of labor resembles damage control aboard a ship. Automatic systems may close a valve immediately, while the decision to abandon a compartment remains with command.
The requirement becomes sharper during conflict. An adversary may deliberately create simultaneous disturbances across a fleet. Even harmless alerts can exhaust the ground team’s attention when presented in sufficient volume. An autonomous system that filters those alerts may preserve command capacity. Yet the same filter can hide a genuine intrusion if its assumptions have been poisoned. Scale makes autonomy necessary while giving a single mistaken policy a much wider blast radius.
Detection Is Easier Than Interpretation
An AI model can recognize statistical departure without understanding operational meaning. This distinction is especially dangerous in space systems because legitimate spacecraft behavior may change abruptly. A safe-mode entry can produce an unfamiliar telemetry pattern. A contingency maneuver can alter power demand. A software update can create a new command rhythm. Each event may look hostile to a model trained on routine flight.
The scarcity of representative attack data sharpens the problem. Commercial network defenders can draw upon large collections of observed malware behavior. Orbital systems provide far fewer public examples of confirmed cyber compromise. Mission-specific hardware also limits the value of general datasets. The model is asked to judge rare events using an incomplete history, which is rather like appointing a magistrate whose legal education consisted of reading the courthouse fire drill.
NIST’s Artificial Intelligence Risk Management Framework recognizes that human and machine roles can range from fully manual judgment to autonomous action. The proper arrangement depends on consequence. For constellation defense, a model’s confidence score cannot settle the matter by itself. Operators must define what a particular confidence level permits the system to do.
This requirement leads toward tiered response. A defensive agent might first restrict a single credential. It could then require stronger authentication for a sensitive command. Only a more severe condition would permit isolation of a spacecraft crosslink. Each step should correspond to a known mission cost. The response ladder converts uncertainty into bounded action.
Reversibility is part of this design. A credential restriction can expire after a specified period unless renewed by another trusted authority. A quarantined data path can reopen through a protected recovery channel. The system should preserve enough evidence for the ground team to reconstruct why the action occurred. NIST’s AI Risk Management Framework Playbook stresses defined human oversight and documentation of operational limits. Those concerns become concrete when the model can remove a satellite from service.
Explainability in this setting does not require a philosophical account of machine cognition. The operator needs a concise operational reason. The system should identify the command that triggered its response. It should show which rule or behavior boundary was crossed. It should also state when the restriction will expire. A bare anomaly score is inadequate because commanders cannot compare that number against mission need.
The proper measure of a defensive agent is therefore wider than detection rate. Evaluation must include false isolation under degraded operations. It must test recovery time after an incorrect response. It must also measure whether a trained operator can understand the system’s action quickly enough to intervene. A model that detects every intrusion while repeatedly disabling healthy spacecraft has produced a splendid shield with the unfortunate habit of striking its owner.
Quarantine as an Exercise of Command Authority
Consider a missile-warning spacecraft during a regional crisis. Its defensive agent observes commands from a valid account, but the sequence differs from the operator’s usual pattern. The agent estimates that the credential may have been stolen. Immediate quarantine would reduce the chance that the intruder reaches another spacecraft. It would also reduce warning coverage at the hour when commanders need it most.
No accuracy threshold can remove the command judgment inside this choice. The decision weighs the risk of compromise against the cost of lost mission capacity. Those values come from operational planning. Engineers may express them through permissions, but the policy belongs to commanders.
Space Policy Directive 5 establishes the expectation that space systems retain positive control through risk-based cybersecurity principles. CISA’s summary of Space Policy Directive 5 also emphasizes protection across the spacecraft and its supporting infrastructure. Positive control becomes more complicated when a defensive agent can reject a command from an authenticated human. The machine is obeying standing authority while refusing immediate instruction.
This apparent contradiction can be managed through predelegation. Commanders should define the defensive actions permitted during routine operations. A separate set of permissions may apply during declared conflict. The authority to block one command need not imply authority to sever every crosslink. Mission planners can assign different limits to different spacecraft according to their role.
Time limits are equally important. An autonomous quarantine should expire unless the system can produce fresh evidence or a human operator confirms the restriction. This prevents an uncertain judgment from becoming a permanent loss. A protected restoration path must remain available even when the ordinary command account is suspect.
The decision record should be preserved beyond the spacecraft. A tamper-evident log can allow investigators to compare the agent’s reasoning with the telemetry available at the time. This record supports accountability after a failure. It also helps trainers determine whether the model acted within policy. Without that evidence, responsibility will dissolve into a quarrel between the software team and the operations floor, a ritual as old as malfunctioning machinery.
Command authority also requires deliberate exercises. Tabletop discussion is insufficient because the crucial failures appear under timing pressure. Operators need live scenarios in which the defensive agent imposes a real restriction on a test spacecraft or a high-fidelity replica. The exercise should force the crew to restore service while the origin of the anomaly remains uncertain. The relevant question is whether the combined human-machine team can preserve the mission, not whether the model wins an isolated benchmark.
The Adversary Can Weaponize Defensive Automation
An intelligent attacker will study the defender’s response thresholds. Repeated probes can reveal which command patterns trigger restrictions. The attacker can then remain below those boundaries or create a signal designed to cause quarantine. In the second case, the defensive model becomes part of the hostile kill chain.
This danger is a form of induced denial of service. The attacker may never gain command authority over the spacecraft. It needs only to persuade the defensive agent that compromise has occurred. If the model responds by isolating the vehicle, the adversary receives the operational effect it wanted without defeating the underlying control system.
CISA’s analysis of Zero Trust in the Space Environment supports continual verification across space infrastructure. Applied carelessly, continual verification can become continual suspicion. A resilient design should allow the system to narrow access before eliminating service. The distinction gives defenders room to contain risk without granting every anomaly the power to remove a spacecraft.
Model corruption presents a deeper threat. The defensive agent may rely on updates prepared through a contractor network. If an attacker alters the training records or configuration package, the model can learn to accept hostile conduct as normal. The compromise then arrives aboard the defender’s own maintenance process.
NASA’s Office of Inspector General warned in its review of NASA’s Management of Artificial Intelligence Capabilities that incomplete governance and weak inventories can hinder the protection of AI data. For space defense, provenance must extend from source data to the model loaded for flight. The operator should know who approved the package. The system should verify its signature before execution. A previous trusted version should remain available for rollback.
Independent safety controls offer another layer of protection. The AI model may recommend or execute a bounded response, while a simpler rule-based system prevents actions outside a defined mission envelope. The rule set can prohibit simultaneous quarantine of too many spacecraft. It can preserve a minimum warning geometry. It can also prevent the model from disabling its own audit channel.
This separation creates purposeful friction. The model retains speed where delay would be dangerous. The safeguard preserves mission boundaries that the model cannot reinterpret. Machine-speed conflict will reward the side whose automation fails cautiously, because an elegant model with unlimited authority can become an amazingly obedient saboteur.
Acquisition and Testing Requirements
Autonomous defense should enter acquisition documents as a mission capability with explicit authority limits. A requirement that merely calls for “AI-enabled cyber defense” says almost nothing. The program must specify what the agent may observe. It must state which restrictions the agent may impose. It must define the conditions for human confirmation.
Testing should include abnormal but legitimate spacecraft behavior. Safe-mode transitions offer a strong case because they often alter telemetry while reducing operator visibility. The defensive agent must avoid treating every degraded state as evidence of attack. It should also recognize when an attacker is using a known contingency pattern as camouflage.
Programs should test adversarial manipulation of the model itself. Red teams can probe thresholds through repeated command attempts. They can corrupt a maintenance package in a controlled environment. They can also attempt to trigger simultaneous quarantines across a representative portion of the fleet. NIST’s work on autonomous cybersecurity and AI risk in uncrewed systems provides a useful bridge between general AI governance and systems that must act with limited human contact.
Contract terms must address the consequences of automated containment. A commercial operator supporting defense missions may face government direction to isolate a spacecraft. Civilian customers could lose service as a result. The agreement should establish who possesses decision authority and who bears the cost of a false quarantine. Silence on this point leaves the hardest command question to a conference call during the crisis, which is where clarity goes to misplace its shoes.
Software support must continue throughout the mission life. Threat assumptions will change after launch. New ground systems will connect to the architecture. The defensive model will require controlled updates, yet every update becomes a supply-chain event. Acquisition policy should therefore fund model monitoring and secure rollback as recurring mission functions.
Strategic and Policy Implications
For defense leaders, autonomous cyber defense moves command judgment earlier in time. The decisive choices will occur when permissions are approved and response thresholds are set. A commander who ignores those settings has still made a decision. The decision has merely been delegated to whoever wrote the default.
For commercial operators, containment authority becomes part of service assurance. A company may need to prove that its defensive agent can protect a military customer without imposing reckless disruption on civilian users. Transparent response boundaries will carry contractual value because customers will want to know when the provider can cut service.
For policymakers, responsibility will become harder to assign. An automated quarantine can cause strategic harm without damaging hardware. If the loss of coverage affects an allied operation, investigators will have to distinguish software error from poor command policy. The distinction matters because each failure demands a different remedy.
Policy should avoid treating autonomy as a single condition. Authority should be described by action. A system permitted to reject a malformed command is operating under a different grant of power from one permitted to isolate a satellite. Clear language will help oversight bodies judge actual risk rather than argue over whether a spacecraft is “autonomous.”
The most useful indicator will be the appearance of live exercises in which defensive agents take containment actions without immediate human confirmation. Such exercises would show that organizations have moved beyond demonstrations of anomaly detection. They would also reveal whether doctrine has caught up with engineering.
Findings and Strategic Estimate
Autonomous cyber defense will become necessary as proliferated constellations exceed the investigative capacity of ground teams. Its earliest operational role will involve narrow containment actions whose effects can be reversed. Credential restrictions are more likely to receive approval before full spacecraft quarantine because they preserve mission capacity while buying time.
The central risk will come from adversarial manipulation rather than ordinary model error alone. An attacker who learns the defender’s thresholds can provoke protective action for hostile effect. Defensive architecture must therefore limit how much mission capacity any one model can remove.
Human judgment will remain decisive, but it will migrate into doctrine and software permissions. Commanders will govern the future constellation through rules established before contact with the enemy. Engineers will express those rules in code. Operators will inherit their consequences during the contact window.
The future constellation will occasionally have to choose between obedience and survival. Spacepower will depend upon who taught it how to choose, what limits were placed upon that lesson and whether a human commander can still recover the spacecraft when the machine chooses poorly.
This is a public episode. If you would like to discuss this with other subscribers or get access to bonus episodes, visit orbitest.substack.com